Security
Authentication
Any uses a cryptographic password hashing technique to secure the storage of the passwords. The credentials of the users are hashed before being saved in the data storage. Hashing the credentials is one of the most common security techniques when protecting the private credentials of a user. The hashing algorithm used is SHA-512. A random salt is added to the hashing process to force their uniqueness, increase their complexity without increasing the requirements on the users and mitigate password attacks like "Rainbow Tables".
To limit brute-force attacks on the password, you can configure a maximum number of failed sign-in attempts. Beyond this limit, the account is blocked and an email is sent to the administrator.
Authentication can also be configured on an external system with SAML, Kerberos and others.
Service security
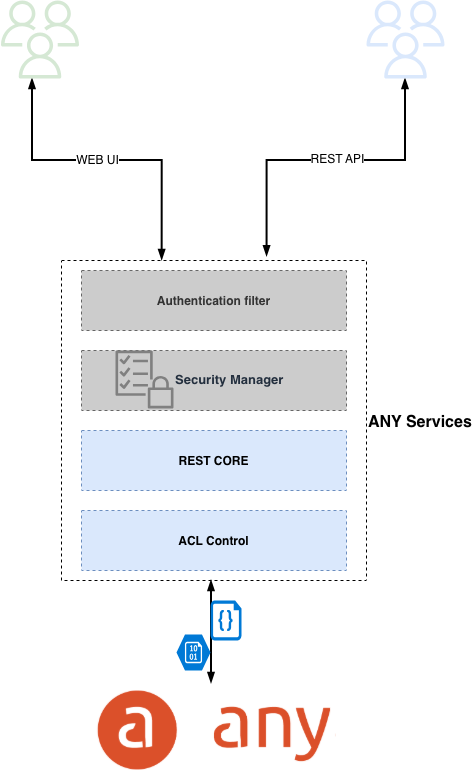
Security is applied in the Any Webapp and intercepts every request. When a service is called, the Security Manager intercepts the request and checks that the user has sufficient permissions to reach the service. The first layer filters the action based on the authentication and the roles of the user. The security of the documents is based on their context. A user can have a write permission from an application and read-only from another. Any has 2 types of permissions:
- Listing permissions, which let a user search documents and view their metadata.
- Advanced permissions, which let the user see the content and run an action on the document.
This separation keeps the search performant and gives a strong, fine granularity for the other permissions. A pre-check is done to avoid the displayed action if the user does not have the correct access. Both types of permissions are constantly checked for every action.
Encryption and access
The high-availability environments require several nodes for MongoDB and Elasticsearch. The Transport Layer Security protocol (TLS/SSL) is used to secure the communication between the nodes and for every incoming and outgoing connection. Every communication is limited to the customer VPC environment, this way the data can only be reached by the server belonging to your VPC. Every public request is rejected.
To strengthen the security, all the data is encrypted at rest.
Every content is automatically encrypted when it is dropped on the S3 storage using the AWS Amazon S3 encryption. When a download is requested, the server automatically decrypts it. The encryption key used is generated and hosted by AWS Amazon S3.